Access & exceptions
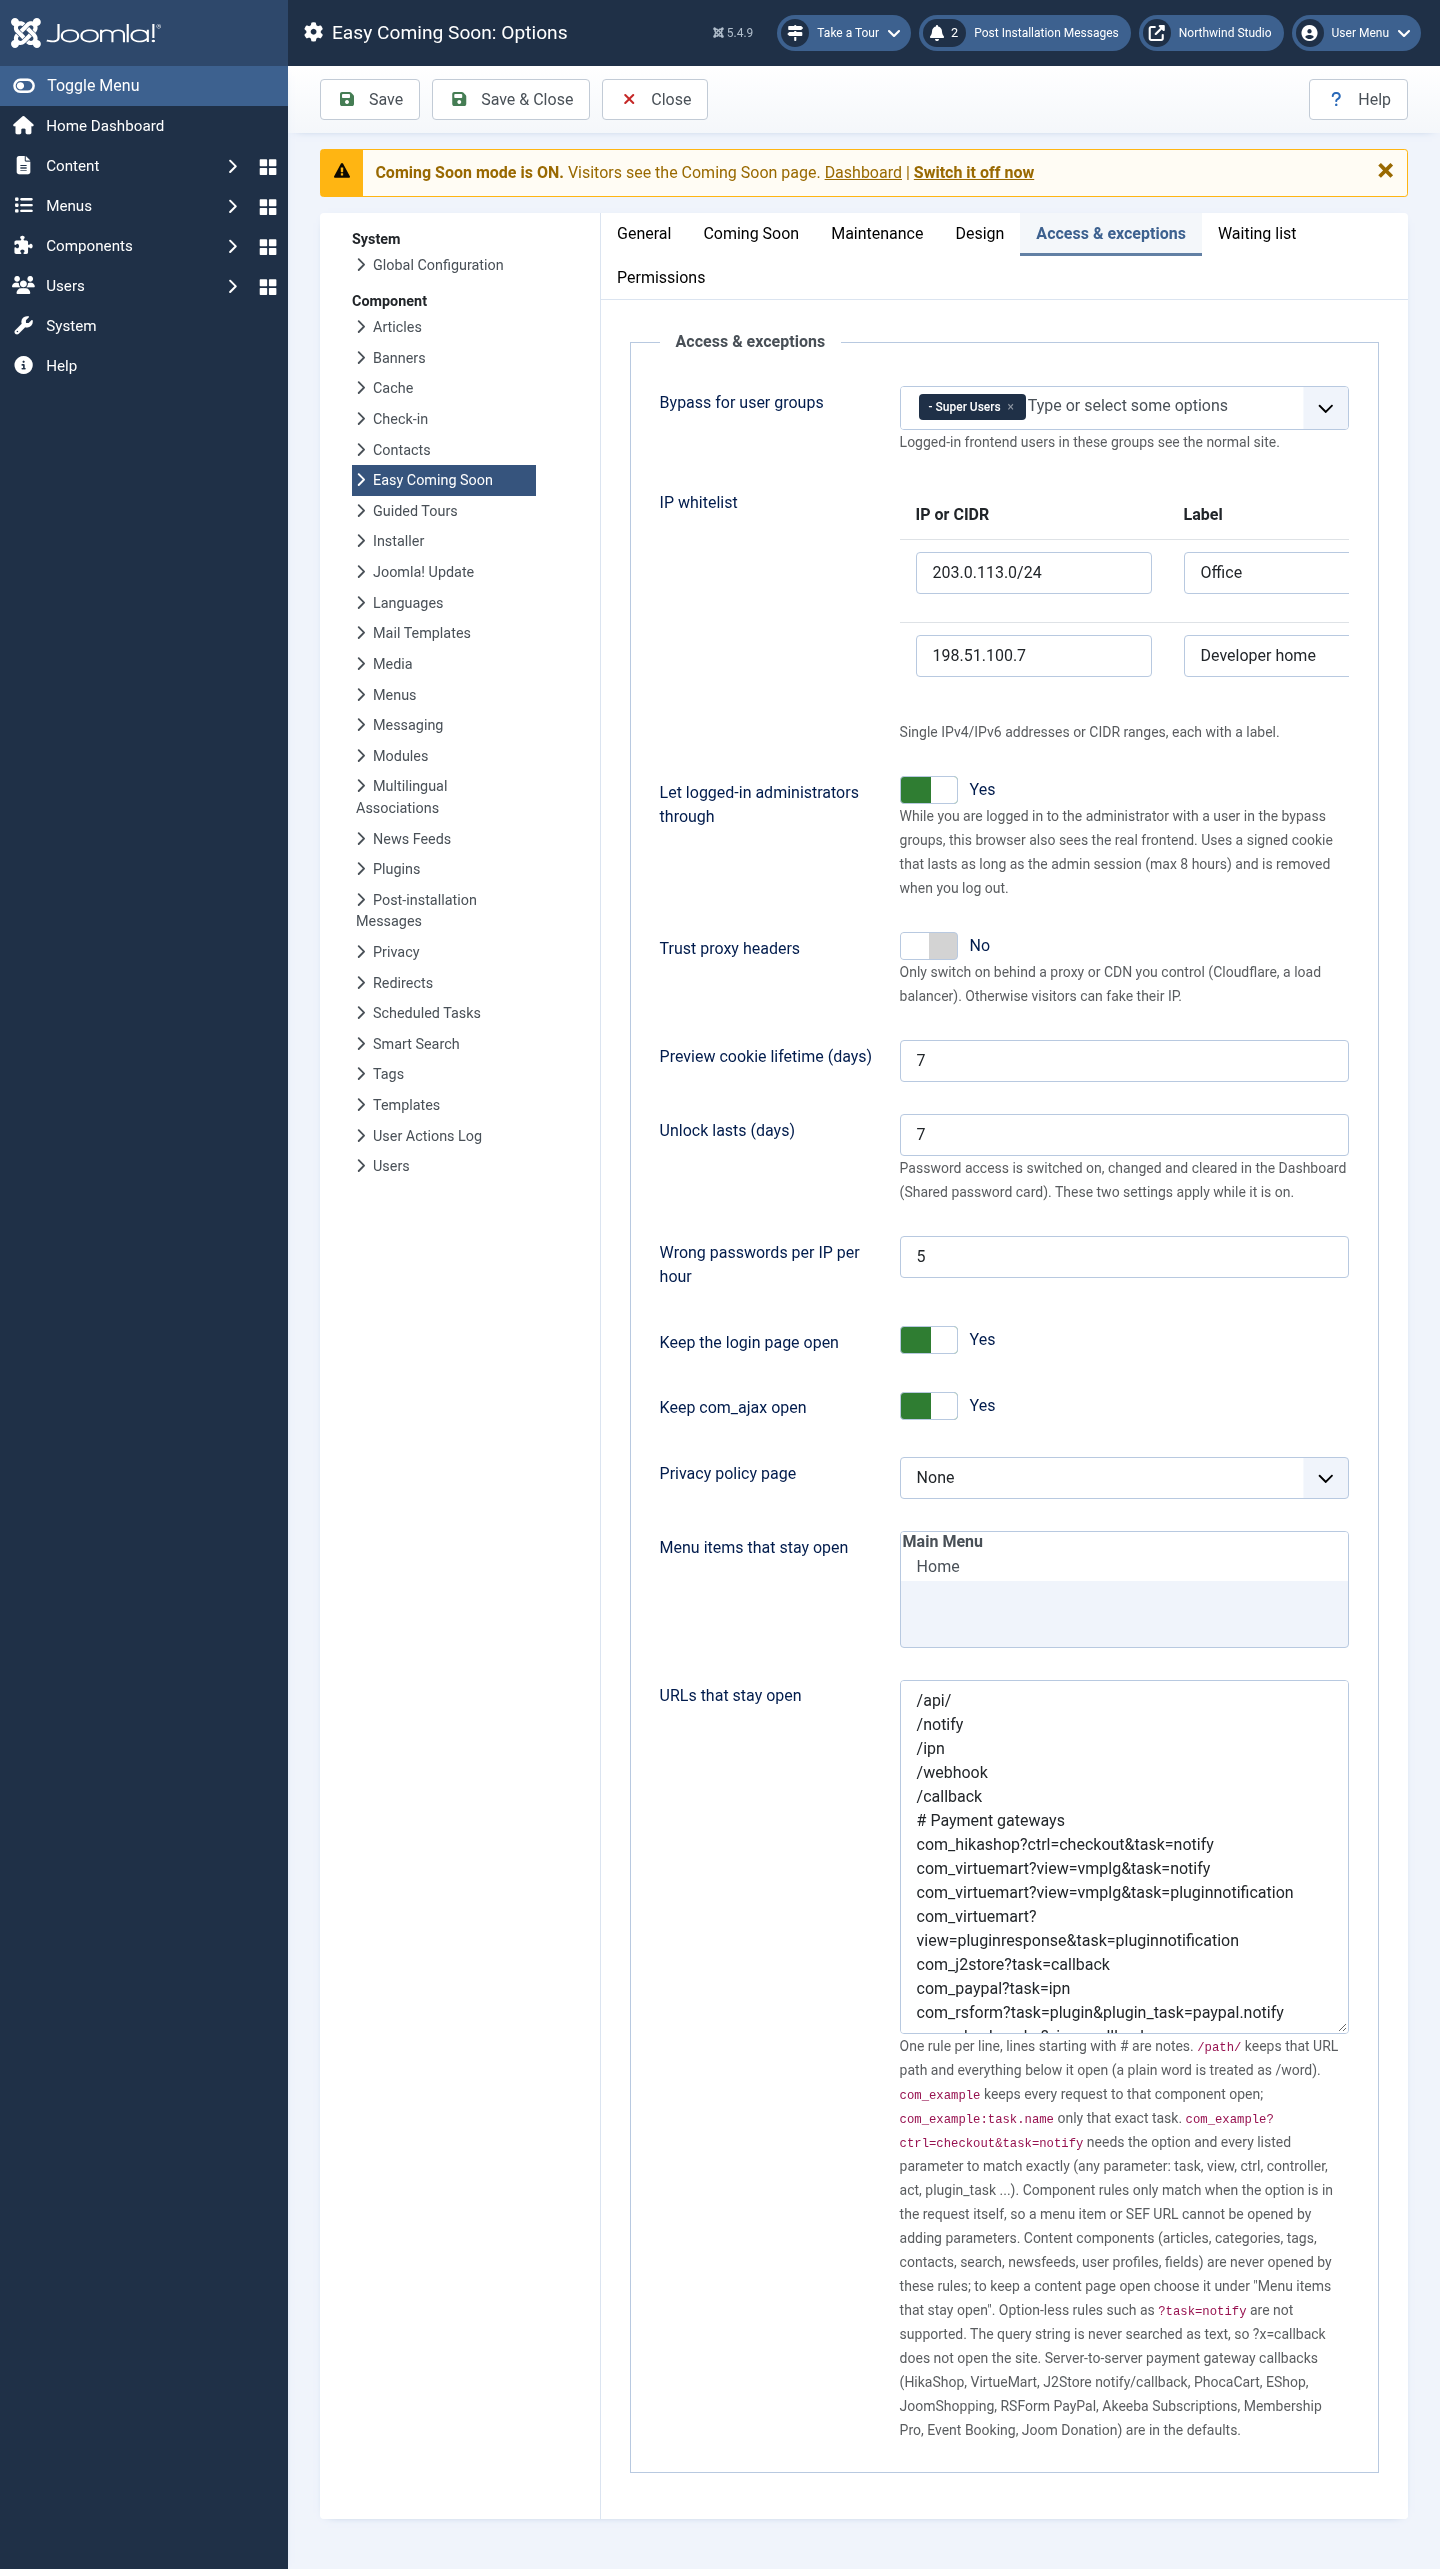
| Setting | Default | What it does |
|---|---|---|
| Bypass for user groups | Super Users | Users in these groups see the real site only when they're logged in on the front end. Child groups are included automatically. An administrator who is logged in only to the backend gets through with Let logged-in administrators through instead (on by default). |
| IP whitelist | empty | One row per IP or CIDR with a Label. IPv4 and IPv6 both work. |
| Let logged-in administrators through | Yes | While you're logged in to the administrator as a user in a bypass group, the same browser sees the real front end. This uses a signed cookie that lasts at most 8 hours, stays tied to your live admin session and is removed when you log out. |
| Trust proxy headers | No | Turn this on only behind a proxy or CDN you control, such as Cloudflare or a load balancer. Otherwise visitors could fake their IP. |
| Trusted proxies in front of the site | 1 (1–10) | How many proxies sit in front of your site. The visitor IP is read that many steps from the right of X-Forwarded-For. |
| Preview cookie lifetime (days) | 7 | How long a preview link keeps working in a visitor's browser. |
| Unlock lasts (days) | 7 | How long a visitor stays unlocked after entering the password. Applies while password access is on. (There's no on/off switch here; use the Dashboard's Password access card.) |
| Wrong passwords per IP per hour | 5 | Slows down password guessing. |
| Keep the login page open | Yes | Keeps Joomla's login, password reminder and reset pages working. |
| Keep com_ajax open | Yes | |
| Privacy policy page | none | This menu item stays open so visitors can read it. (It is not linked from the page automatically; add a link in your page text if you want one.) |
| Menu items that stay open | none | Pick pages that stay public. |
| URLs that stay open | see section 7 | Allow rules. |
The order of checks. A visitor sees the real site if any of these match, checked in this order:
- a bypass user group (logged in on the front end)
- the IP whitelist
- a preview link cookie (the main link or a named link)
- the password unlock cookie
- the administrator session cookie
The Joomla administrator, the Joomla API (/api/) and the command line are never blocked.